
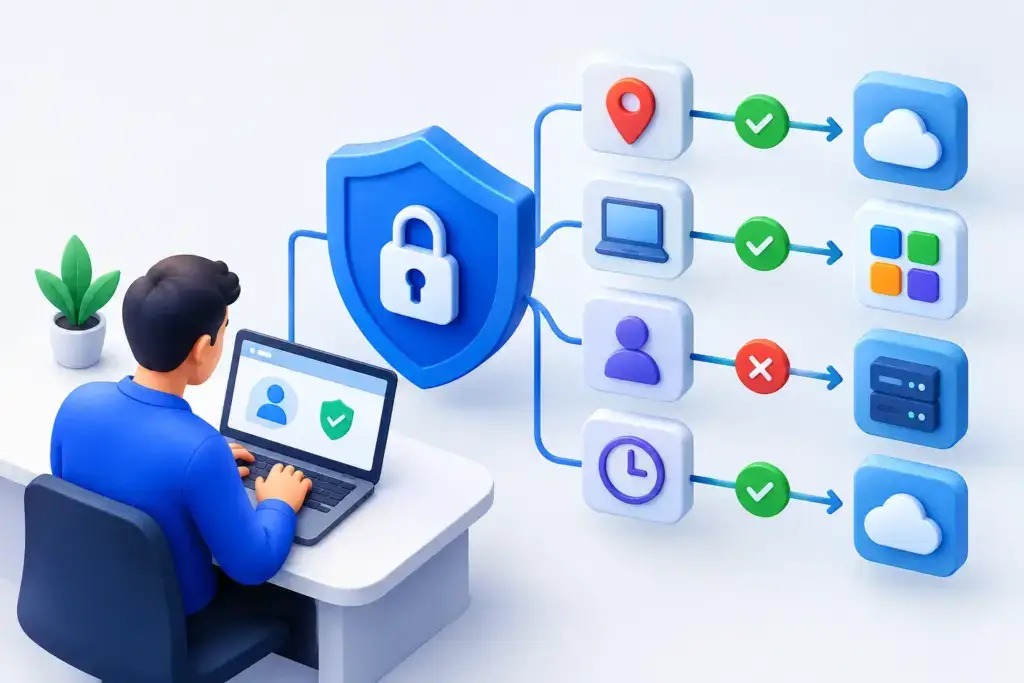
A stolen password should not be enough to reach your company’s email, files, finance systems, or customer data. Yet for many small and mid-sized businesses, that is still the practical reality. When you configure conditional access policies in Microsoft Entra ID, you add context to every sign-in decision: who is signing in, from what device, from where, and under what level of risk.
Conditional Access is one of the most effective controls available in a Microsoft 365 environment, but it can also create real disruption when it is rushed. A poorly scoped policy can lock out leadership, break a line-of-business application, or interrupt access for a remote employee on the first day of a critical project. The objective is not to block everything. It is to make legitimate work easier to verify and risky access harder to complete.
What Conditional Access Actually Changes
Microsoft Entra Conditional Access works as an if-then decision engine. If a sign-in meets selected conditions, then Microsoft requires a control such as multifactor authentication (MFA), a compliant device, a password reset, or a blocked sign-in.
That distinction matters because MFA alone is not a complete access strategy. MFA is a foundational control, but the same prompt does not make sense for every person, device, location, application, or risk level. An employee using a managed laptop in the office may need a different experience than someone attempting to access SharePoint from an unknown personal computer halfway around the world.
For business leaders, the payoff is straightforward: better protection without forcing every employee into the same restrictive workflow. For internal administrators, the benefit is consistency. Access decisions become documented policies rather than one-off exceptions, informal workarounds, and late-night support calls.
Before You Configure Conditional Access Policies
Start with visibility, not enforcement. Conditional Access affects identity, and identity is connected to nearly every cloud service your team relies on. Before creating policies, review who has administrative roles, which accounts are shared, what applications use noninteractive sign-ins, and whether employees access company resources from personal devices.
You also need to confirm licensing and technical readiness. Conditional Access requires the appropriate Microsoft Entra ID licensing, typically Microsoft Entra ID P1 or P2 depending on the features you plan to use. Device compliance policies and risk-based protections may introduce additional requirements through Microsoft Intune and Entra ID P2.
The most common mistake is treating Conditional Access as a single security switch. It is a policy framework. The right configuration depends on your organization’s users, regulatory obligations, device-management maturity, and tolerance for friction. A 25-person professional services firm with company-issued laptops can often require compliant devices more quickly than a 200-person operation with contractors, shared workstations, and legacy applications.
Before enforcement, establish two emergency access accounts. These are tightly protected cloud-only administrator accounts, excluded from routine Conditional Access policies and monitored closely. They exist for a worst-case scenario, such as a configuration error, an identity outage, or a failed federation service. They are not convenience accounts and should never be used for daily administration.
Build Policies Around Business Risk
A strong rollout begins with a small set of high-value policies. Do not create ten overlapping rules simply because the portal allows it. Each policy should have a clear business purpose, an owner, a documented exception process, and a review date.
For most organizations, the initial policy set addresses four priorities:
- Require phishing-resistant MFA or approved MFA for administrators.
- Require MFA for all users accessing Microsoft 365 and other cloud applications.
- Block legacy authentication protocols that cannot support modern sign-in controls.
- Require managed or compliant devices for sensitive applications and data where the business is ready to enforce that standard.
Administrator protection should come first. Privileged accounts can change users, licenses, policies, devices, and security settings. Requiring stronger authentication for administrators is a practical way to reduce the likelihood that a single compromised password becomes a company-wide incident. Where possible, use phishing-resistant methods such as FIDO2 security keys, passkeys, or certificate-based authentication rather than relying only on push notifications.
Blocking legacy authentication is equally important. Older protocols can bypass modern authentication and MFA protections. Attackers know this, which is why password-spray attempts often target older mail clients and protocols. Before blocking them, verify whether scanners, copiers, older applications, or service accounts still depend on them. The answer may be to modernize the connection, use a supported relay method, or isolate a necessary exception while a replacement is planned.
A Practical Configuration Process
In the Microsoft Entra admin center, create policies in report-only mode whenever possible. Report-only mode lets you see how a policy would affect sign-ins without enforcing it. This turns assumptions into evidence and gives your IT team time to find edge cases before employees find them during business hours.
Start with named groups
Use groups to make policy assignments understandable. Create or verify groups for administrators, standard employees, contractors, high-risk departments, and approved exception users. Avoid assigning policies person by person unless there is a temporary, documented reason.
Groups also make the policy easier to manage as your company grows. When a new finance employee joins, their access requirements should follow the role or department group, not depend on someone remembering to edit three separate policies.
Select users, applications, and conditions carefully
A Conditional Access policy generally asks three questions: who is making the request, what are they trying to access, and under what circumstances? Scope is everything.
For an initial all-user MFA policy, target all users while excluding the emergency access accounts. Apply it to the cloud applications you intend to protect, often all cloud apps after compatibility testing. Then require MFA as the grant control.
Conditions can add meaningful precision. You may evaluate device platform, client application, location, device state, sign-in risk, or user risk. However, conditions should solve a defined problem. Blocking all access outside the United States, for example, may sound sensible until an executive travels, a vendor support team operates abroad, or a trusted service uses international infrastructure. Country restrictions can help, but they are not a substitute for strong authentication and managed endpoints.
Use compliant devices where it matters most
Requiring a compliant device is powerful because it connects identity protection to endpoint health. A compliant device can be required to have encryption enabled, current security updates, an approved operating system, endpoint protection, and defined screen-lock settings.
The trade-off is operational readiness. If your organization has not enrolled and managed its devices through Intune or another endpoint platform, enforcing compliance immediately will block legitimate staff. A measured approach is to require compliant devices first for high-impact resources such as finance portals, executive data, or administrative consoles. Expand coverage after device enrollment and support processes are stable.
For bring-your-own-device environments, app protection policies may be a more practical starting point. They can protect corporate data inside approved mobile applications without requiring full device management. The right answer depends on the sensitivity of the data, the employee experience you need to preserve, and your compliance obligations.
Test the Real-World Sign-In Paths
Report-only results and sign-in logs are essential, but they do not replace hands-on testing. Test with representative accounts: a standard employee, an administrator, a remote worker, a mobile user, a contractor, and a user who accesses a critical third-party application.
Check more than Outlook and Teams. Test shared mailboxes, mobile apps, printers, conference-room devices, VPN access, single sign-on applications, and automated processes. If an application breaks, do not immediately create a broad exclusion. Find out whether it uses unsupported authentication, an outdated connector, or an account that should be replaced with a properly governed service identity.
When a policy moves from report-only to enabled, communicate the change in plain language. Tell employees what will change, why it is happening, what they should expect on their devices, and where to get help. Security controls work better when people understand that the goal is to protect the company and keep their work moving.
Monitor, Review, and Retire Exceptions
Conditional Access is not a set-it-and-forget-it control. Review sign-in logs after each policy change and investigate repeated failures, unfamiliar locations, impossible travel indicators, and sign-ins that are blocked by unexpected policies. Logs reveal whether a control is stopping threats, causing avoidable friction, or both.
Exceptions deserve special attention. Every exclusion creates a gap, even when it is justified. Document the business reason, the responsible owner, the compensating controls, and an expiration date. A temporary exception for a legacy application should lead to a modernization plan, not become permanent background risk.
As your business changes, your policies should change with it. New acquisitions, remote hiring, compliance requirements, device refreshes, and cloud migrations all affect how access should be governed. This is where a managed security partner can bring value: not just by watching alerts, but by aligning identity controls with the way your people actually work.
The best Conditional Access policy is rarely the strictest one. It is the one your business can consistently enforce, your employees can understand, and your leadership can defend when a security incident or audit puts every access decision under a microscope.
